
Your desktop isn't yours anymore. It's a hunting ground for mercenary spyware and data brokers who treat your private life like a harvestable resource. You feel the weight of those hidden tracking pixels every time you open a browser. Most so-called privacy apps just move the problem; they stop others from spying only to upload your data to their own servers. That isn't protection. It's a handoff. The Spyware Slayer Desktop App changes the rules of engagement. It's a tactical shield built for the digital siege we live in right now.
You're right to be tired of security tools that demand your trust while hoarding your logs in the cloud. You deserve a defense that actually stays on your machine. This article shows you how to deploy a local-first system that neutralizes trackers and data brokers instantly. We'll explore how to get real-time alerts for outbound data leaks and achieve total invisibility from predatory entities. It's time to stop being a target and start being a ghost. Let's reclaim your digital sovereignty and dismantle the surveillance economy on your own hardware.
Key Takeaways
- Stop trusting the cloud; local-first execution is the only way to ensure your privacy audit doesn't become another data leak.
- Identify and neutralize "shadow communications" in real-time before unauthorized data transfers can leave your network.
- Harden your system using the 'Paranoid' profile and Geofence Defense to kill OS-level location tracking at the source.
- Use the Spyware Slayer Desktop App as your tactical shield to dismantle the surveillance economy on your own hardware.
- Initiate your defense with a Free Exposure Report to pinpoint exactly which brokers are currently harvesting your life.
The Digital Siege: Why Standard Security Is a Sieve
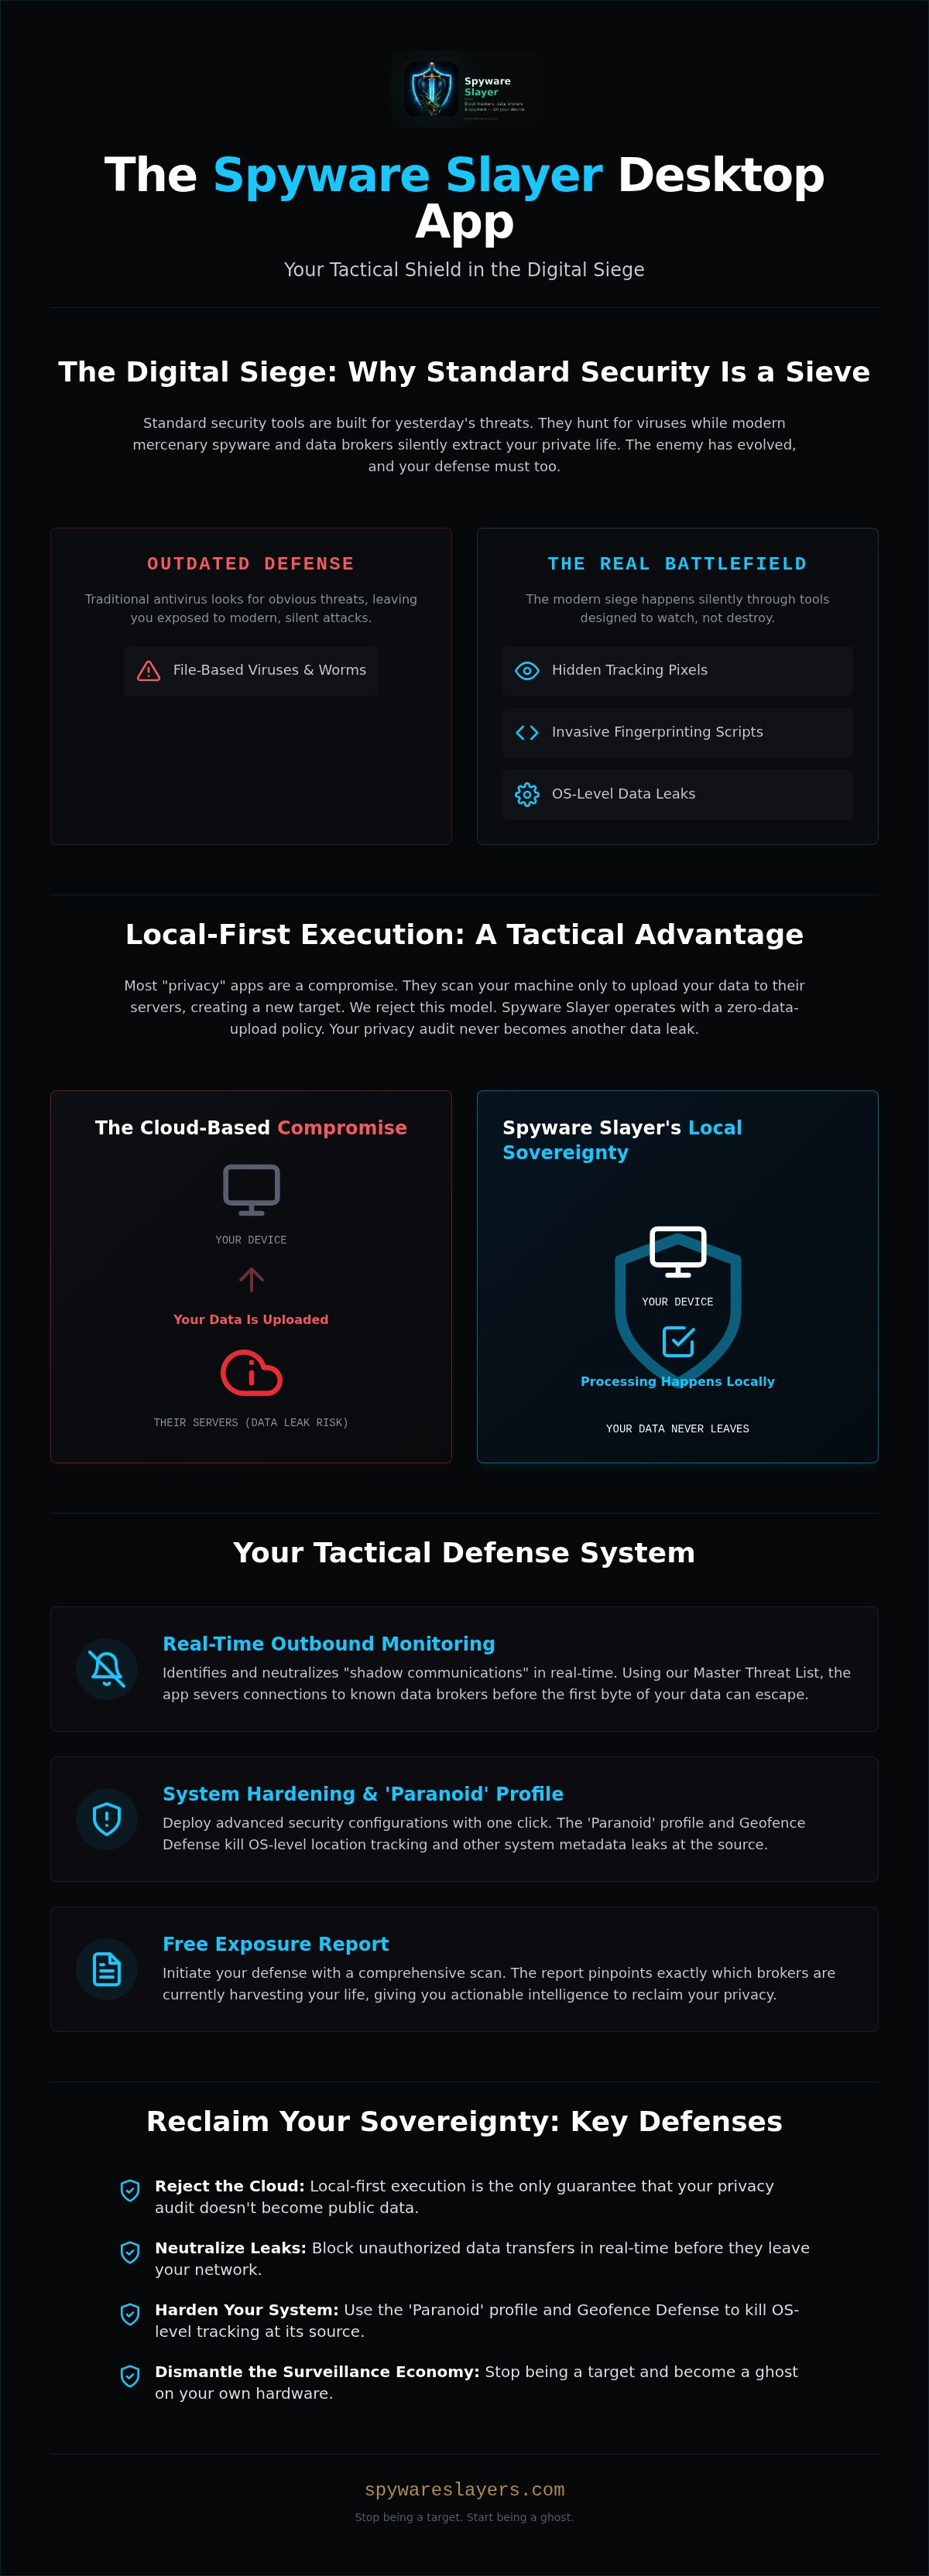
Your desktop is a battlefield. You are the target. Most users believe they're safe because a "security" dashboard shows a green checkmark. They're wrong. Standard security tools are built for the threats of 2010. They hunt for file-based viruses and crude worms. But the enemy has evolved. Modern surveillance is silent. It's the extraction of your life, one pixel at a time. This is the Digital Siege. It's a state of constant, quiet war where your data is the primary casualty.
Tracking pixels and invasive scripts are the new ghosts in your machine. They don't want to crash your system; they want to live in it. They watch your mouse movements. They log your keystrokes. They map your social graph. While you wait for a virus alert that never comes, the Spyware Slayer Desktop App is built to see what these "standard" tools ignore. The siege is already inside your perimeter through:
- Hidden tracking pixels that fire every time you open an email.
- Invasive scripts that fingerprint your hardware to track you across the web.
- Background processes that leak your system metadata to third-party brokers.
The Rise of Mercenary Spyware
Mercenary spyware like Pegasus used to be a threat reserved for heads of state or high-value activists. Not anymore. The technology has trickled down. It's now a commodity bought and sold by corporate entities and aggressive data harvesters. These tools don't ask for permission. To understand the depth of this threat, one must ask: What is Spyware? It's no longer just a nuisance. Mercenary spyware is a predatory entity that bypasses standard OS permissions to turn your microphone, camera, and files into a live feed for the highest bidder. Your personal device is now a window for state-level tracking tactics used by private firms.
The Data Broker Dossier
Every click you make creates a "Digital Wound." Data brokers use automated scrapers to salt that wound, packaging your search history and location into a permanent dossier. Think blocking trackers in your browser is enough? It isn't. The extraction happens at the OS level, hidden in background processes you can't see or stop with a simple plugin. These brokers don't just want your name; they want your predictable future. The Spyware Slayer Desktop App treats this like a tactical extraction. It doesn't just block; it neutralizes. You need a shield that understands the battlefield of 2026, where the "ghosts" are actually data brokers stealing your sovereignty. It's time to stop being a target and start being a ghost.
Spyware Slayer Desktop App: Local Execution as a Tactical Advantage
The cloud is a compromise you can no longer afford. Most "privacy" tools on the market are actually data harvesters in disguise. They scan your system and then upload the results to their own servers. This creates a massive target for hackers and government subpoenas. The Spyware Slayer Desktop App rejects this model. It operates with a zero-data-upload policy. Every scan, every detection, and every block happens locally on your hardware. Your CPU performs the work. Your RAM holds the data. Nothing leaves your machine.
Reclaiming hardware agency is about power. For too long, your computer has been forced to run scripts that benefit trackers and data brokers. By shifting to local execution, you turn your machine into a fortress. It's the only way to ensure your privacy audit doesn't become the next data leak. Before you dive deep into hardening your system, you should check your current vulnerability levels with a Free Exposure Report to see what is already leaking.
Cloud-Based Risks vs. Local Sovereignty
There is a bitter irony in privacy apps that collect telemetry on their users. They claim to protect you while building their own database of your habits. Local execution eliminates this risk by minimizing the attack surface. If your data never reaches a server, it can't be stolen from one. Local processing is the gold standard for 2026 privacy because it removes the middleman entirely. This aligns with official government advice regarding the reduction of surveillance footprints. You shouldn't have to trust a company when you can trust your own encrypted drive.
The Master Threat List
To fight a war, you need intelligence. Our Master Threat List is a tactical briefing updated for 2026 threats. It identifies thousands of data-harvesting scripts and mercenary spyware signatures. This isn't a static file. It's a living database that feeds into the Spyware Slayer Desktop App to provide real-time outbound connection monitoring. When an app tries to talk to a known broker, the connection is severed before the first byte leaves. We categorize threats by their behavior, not just their name. This ensures that even new, unnamed scripts are neutralized the moment they attempt to breach your sovereignty. You aren't just blocking ads. You're dismantling the infrastructure of the surveillance economy on your own terms.
Neutralizing the Invisible: Real-Time Outbound Monitoring
Your computer is leaking. Right now. Most firewalls are designed to stop intruders from getting in, but they're useless against the data already flowing out. This is "Dark Traffic." It's the silent scream of your private information being auctioned off to the highest bidder. This "Shadow Communications" problem is pervasive. Apps you trust are whispering to servers you never authorized. The Spyware Slayer Desktop App acts as a tactical interceptor. It doesn't just watch; it kills. It provides a real-time monitor that visualizes every connection attempt. If an app tries to talk to a server you didn't authorize, the connection is severed instantly. No questions. No compromises.
Standard security tools treat this outbound flow as "telemetry" or "crashes." We treat it as theft. By the time a traditional firewall flags a connection, your data is already halfway across the globe. You need a tool that operates at the speed of the threat. Our local-first architecture ensures that the decision to block happens on your machine, not after a round-trip to the cloud. You regain control over your network interface. You decide who talks to your hardware.
Tracking Pixels and Invasive Scripts
They hide in plain sight. A tracking pixel is a single, invisible dot in an email, a document, or a "privacy-friendly" website. Once opened, it pings a remote server. It tells them your IP address, your device type, and your reading habits. This isn't just marketing; it's tactical surveillance. Following tactical security best practices means assuming every file is a potential beacon. Our Master Threat List identifies the fingerprints of these harvesters in real-time. We neutralize cross-site tracking that tries to follow your identity across the web. We cut the cord before the data leaves your network.
Broker Removal and Extraction
Blocking the leak is only half the battle. You have to clean up the mess they already made. Data brokers have likely already built a dossier on you. They know where you live. They know what you buy. The Spyware Slayer Desktop App includes automated protocols to identify these predatory entities. We call this the "Extraction Order." It's a systematic process to reclaim your identity from broker lists. The first step in this triage is getting your Free Exposure Report. This report pinpoints the specific brokers who have your data right now. Once identified, the app helps you initiate the removal process. Stop the bleeding. Reclaim your sovereignty. This is the resistance.
Tactical Configuration: Deploying the 'Paranoid' Profile
Deployment is the difference between a victim and a survivor. Installing the Spyware Slayer Desktop App is your first step. Configuring it is where you reclaim your agency. You don't leave your front door unlocked at night. Why leave your digital perimeter open to every predatory script on the web? Hardening your system requires a methodical approach to eliminate every possible leak. This isn't a "set and forget" utility. It's a tactical tool that requires precise calibration to achieve total invisibility.
Before you engage the most aggressive protocols, you must understand your baseline. Most users are shocked to see how many connections their machine attempts in a single minute. Your first priority is triage. You need to identify which brokers already have a foothold in your system. Start by running a Free Exposure Report to see what's already leaking. Once you have your targets, you can begin the hardening process with these tactical steps:
- Activate Geofence Defense to kill OS-level location pings.
- Load the latest Master Threat List to identify known harvesters.
- Toggle the 'Paranoid' profile for maximum outbound blocking.
- Review the Real-time Monitor to audit every active connection.
Geofence Defense Setup
Your desktop is constantly broadcasting your coordinates. It isn't just about GPS. It's your IP address, your Wi-Fi SSID, and OS-level pings that leak your physical location. Marketing scrapers use this data to build a map of your life. Geofence Defense kills these pings at the source. It ensures your machine doesn't "phone home" with your coordinates every time you wake it from sleep. You become a moving target that can't be pinned down. This is about physical security in a world that treats your location as a commodity.
The Paranoid Profile Protocol
The 'Paranoid' profile is our most aggressive defensive stance. It's designed for high-stakes environments where a single leak is a total failure. This protocol blocks all outbound traffic by default. It's total stealth. Every application must justify its existence before it's allowed to communicate. For remote workers, it provides a sanctuary from corporate telemetry and invasive tracking scripts. It creates a "clean room" environment on your own hardware.
Managing real-time alerts is the key to success. You need to identify threats without suffering from security fatigue. The Spyware Slayer Desktop App categorizes these alerts based on the Master Threat List, allowing you to dismiss safe connections while neutralizing predatory ones. You see the destination. You see the intent. Then, you decide if that connection lives or dies. This is how you reclaim your hardware from the ghosts in the machine.
Founding Access: Joining the Digital Resistance
The siege doesn't end. It evolves. Mercenary spyware developers don't sleep. Neither should your defense. A subscription model isn't just a billing cycle. It's a logistical supply chain for your digital sovereignty. New trackers emerge every hour. The Spyware Slayer Desktop App requires a continuous stream of intelligence to keep its Master Threat List effective. Without these updates, your shield becomes a relic of yesterday's war. You need a persistent defense for a persistent threat.
Founding Access is a limited window for the digital resistance. It's for those who demand long-term sovereignty at early-adopter rates. This isn't just about software. It's about reclaiming your agency from the surveillance economy. By joining now, you secure your place in a local-first movement that rejects the cloud entirely. You move from being a harvestable resource to being a protected entity. Your hardware finally works for you, not the brokers.
The Founding Access Mission
When you secure Founding Access, you're backing an independent privacy movement. You get priority access to tactical features like advanced script lockdown and the latest Geofence Defense protocols. Founding members are the vanguard. They help shape the future of the Master Threat List by providing telemetry-free feedback on new predatory entities. You aren't just a customer. You're a partner in dismantling the infrastructure of silent extraction. This is how we build a web that respects boundaries.
Your First Extraction
Your first 30 days will be a revelation. We call the initial scan the "Extraction Order." You'll watch in real-time as the app identifies and neutralizes trackers that have lived in your machine for years. You'll finally see your "Digital Wound" score. This score represents the depth of the dossiers brokers have built on your habits. During your first month, you'll watch that score drop as you initiate Broker Removal protocols.
Interpreting your privacy stats becomes a daily tactical briefing. You'll see exactly which apps tried to leak your location and which scripts were killed before they could ping a remote server. You'll move from a state of total exposure to a state of reclaimed agency. The ghosts in the machine are evicted. Your desktop becomes a fortress again. Secure your Founding Access and neutralize the trackers today.
Reclaim Your Digital Sovereignty
The digital siege is real. It doesn't have to be your reality. You've seen how standard security fails to stop the silent extraction of your life. You know that local execution is the only way to ensure your data stays where it belongs; on your machine. By deploying the Spyware Slayer Desktop App, you move from being a target to being a ghost. You gain the power of real-time outbound connection monitoring and a Master Threat List updated for 2026 threats. No cloud uploads. No compromises. Just pure, tactical defense.
Stop the bleeding. Reclaim your hardware from the data brokers and mercenary scripts that treat your privacy like a product. You have the tools. You have the intelligence. Now, you need the shield. Secure your perimeter and join the resistance. It's your machine. It's your life. Take it back.
Claim Your Founding Access and Kill the Trackers
Your digital sovereignty starts now. Don't wait for the next breach.
Frequently Asked Questions
Does the Spyware Slayer Desktop App replace my antivirus?
No, it isn't a replacement for antivirus software. Antivirus hunts for old-world file infections and malware. The Spyware Slayer Desktop App is a tactical shield for your privacy. It hunts for silent data extraction, tracking pixels, and mercenary spyware that standard tools ignore. You should use both to ensure a total perimeter defense. One stops the virus; we stop the leak. It's about protecting your sovereignty, not just your files.
What does 'local execution' actually mean for my data?
Local execution means your data never leaves your hardware for processing. Most "privacy" tools upload your logs to the cloud, creating a new target for hackers and state-level subpoenas. We process everything on your own CPU and RAM. Your privacy audit stays on your machine, encrypted and inaccessible to us or anyone else. It's the only way to ensure your defense doesn't become another data leak. Your machine works for you.
Can this app detect Pegasus or other mercenary spyware?
Yes, the app is engineered to identify the signatures and behavioral patterns of mercenary spyware like Pegasus. These predatory entities bypass standard OS permissions to turn your device into a surveillance beacon. By monitoring outbound connections in real-time, we detect the "shadow communications" these tools use to exfiltrate your data. We don't just alert you; we kill the connection instantly to maintain your sovereignty. You stop being a target and start being a ghost.
How does the Geofence Defense stop location tracking on a desktop?
Geofence Defense hardens your physical privacy by intercepting OS-level location pings before they reach the web. Desktops often broadcast your coordinates via Wi-Fi SSIDs and IP-based metadata. We block these requests at the source. This stops marketing scrapers and data brokers from linking your home address to your digital activity. You control when and if your machine broadcasts its physical location. It's about physical security in a world that treats your location as a commodity.
Will the real-time monitor slow down my computer's performance?
Performance impact is negligible because the app is built for efficiency, not corporate bloat. Our real-time monitor is a lightweight tactical tool that operates at the kernel level to watch outbound traffic. It doesn't perform heavy file scanning like traditional security software. Your CPU works for you, not the trackers. Most users find their system actually feels faster once invasive tracking scripts are neutralized and blocked from consuming your hardware resources.
What is the 'Master Threat List' and how often is it updated?
The Master Threat List is our proprietary intelligence database of known data brokers, tracking pixels, and mercenary spyware signatures. It's updated continuously to neutralize new threats as they emerge in 2026. This isn't a static list; it's a living record of the surveillance economy's infrastructure. Every update is pushed to your app to ensure your shield remains effective against the latest predatory extraction tactics. We hunt the hunters so you don't have to.
Is there a free version of the Spyware Slayer app available?
Yes, a core version of the Spyware Slayer Desktop App is available for download. We believe basic privacy sovereignty shouldn't be a luxury. This version provides essential tracker blocking and detection to get you started in the resistance. For those in high-stakes environments, we offer "Founding Access" and premium features. These include automated broker removal and the "Paranoid" profile for users who need the most aggressive defense against sophisticated mercenary threats.
How do I use the Free Exposure Report to find data brokers?
Your Free Exposure Report is the first step in the triage process. You initiate the report through the app to scan public databases and known broker lists for your personal information. It generates a "Digital Wound" score that shows exactly how much of your life is currently being harvested. Once you see the targets, you can use our Broker Removal tools to start the extraction and reclaim your identity from their dossiers.